How do you create an API endpoint
Design
- Define the decision logic you want to solve with Decisimo. Then prepare the data you will send to the decision engine. As a rule, send all data you have for the situation you want to evaluate.
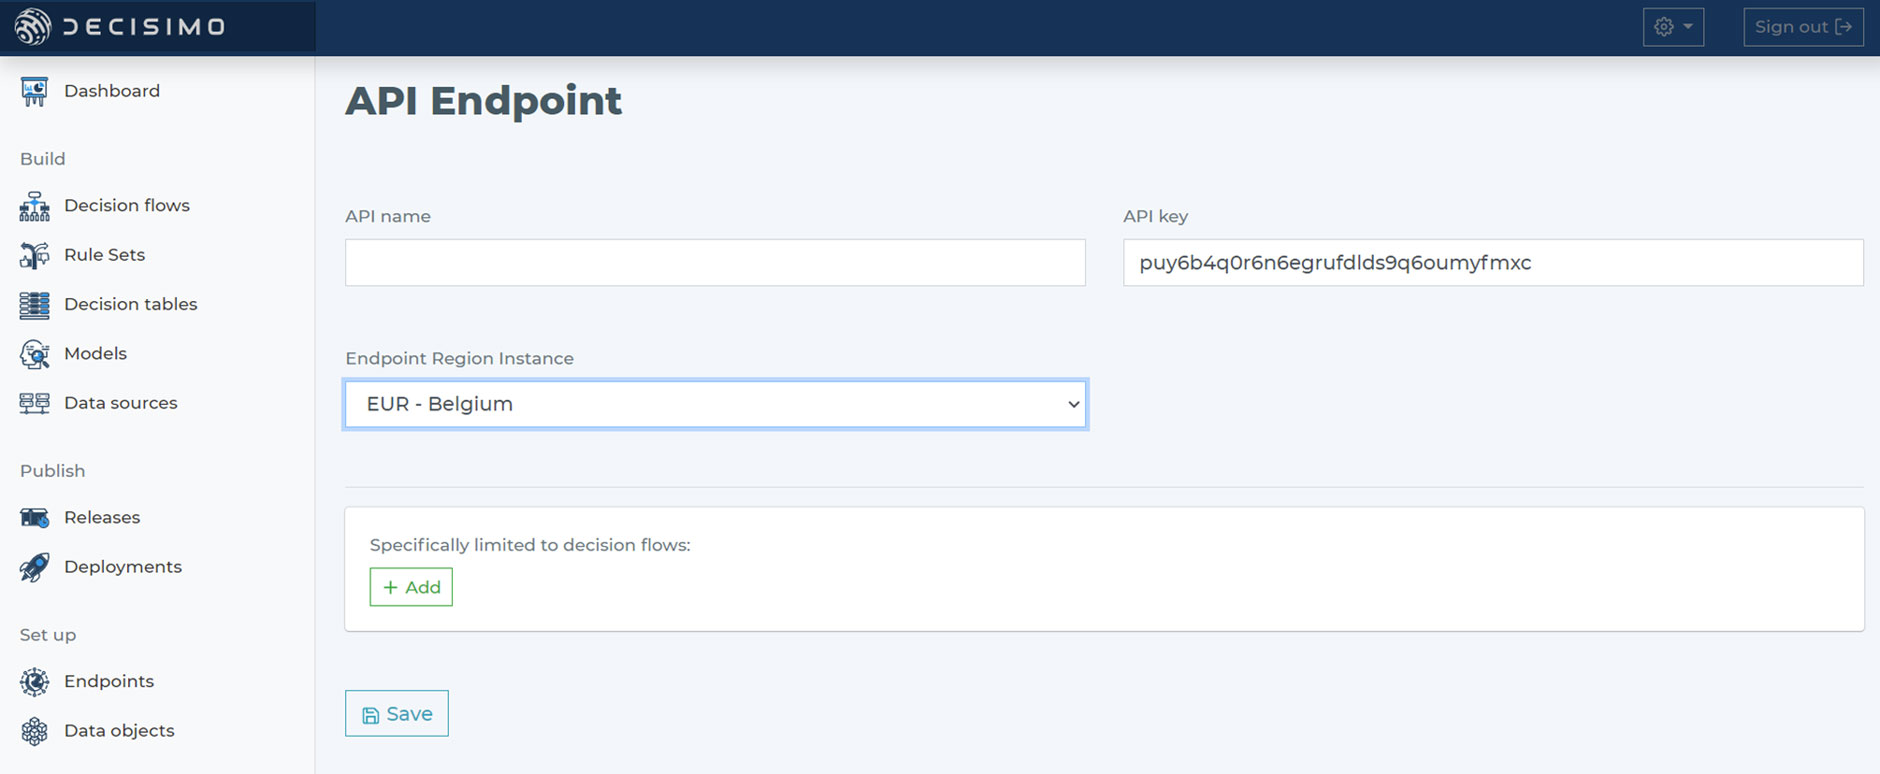
Selecting instance region
- When you choose an endpoint region for the API endpoint, base the choice on data privacy and protection rules. The instance is where your API endpoint will be established.
You can create as many endpoints as you need in different regions.
Testing endpoint
- Because you can create multiple endpoints, create separate ones for testing and production. Before you deploy a new decision flow to production, test it on the testing API endpoint with your preferred tool, such as Postman or SoapUI.

Request and Response payload
- Decisimo API endpoints consume JSON input sent with the POST method. The response is also JSON. It returns the same JSON, enriched or changed within the decision flow.
Deploy your decision flow
- Build your first decision flow and deploy it to your endpoint to start automated decision making.
Frequently asked questions
How much input data should I send to a decision API endpoint?
Send only the fields the decision logic needs to produce its outcome. Map each input to a rule or calculation, and define how the endpoint should handle missing or invalid values. Avoid sending a whole customer record by default. Unnecessary fields increase exposure and make the input contract harder to maintain.
Should I use separate API endpoints for testing and production?
Yes. Keep a testing endpoint separate from the production endpoint so test requests cannot affect live decisioning. Test the intended release against representative inputs, record which release you tested, and confirm the intended release is deployed to production. Keep test credentials and traffic separate too.
What security checks should I complete before connecting an application to the endpoint?
Use the endpoint’s supported authentication and network controls, and store credentials in a secrets manager rather than application code. Confirm that the calling application sends requests over an encrypted connection, then test that unauthorized requests are rejected. Rotate credentials according to your organization’s security policy.
